Why Per-Request Authorization Is the Foundation of Zero Trust

Sterling Davis
Head of Product Marketing
Head of Product Marketing
Most access tools treat authentication like a one-time handshake. In these models, once a user or service is validated, they’re granted broad access for the rest of their session, regardless of what changes afterward.
This worked when everything lived behind a firewall. But today, it’s a liability.
Traditional session-based access creates blind spots, especially when sessions persist for hours or days. It breaks the Zero Trust model.
Per-request authorization means that every request, not just the first, is evaluated, in real-time, against policies.
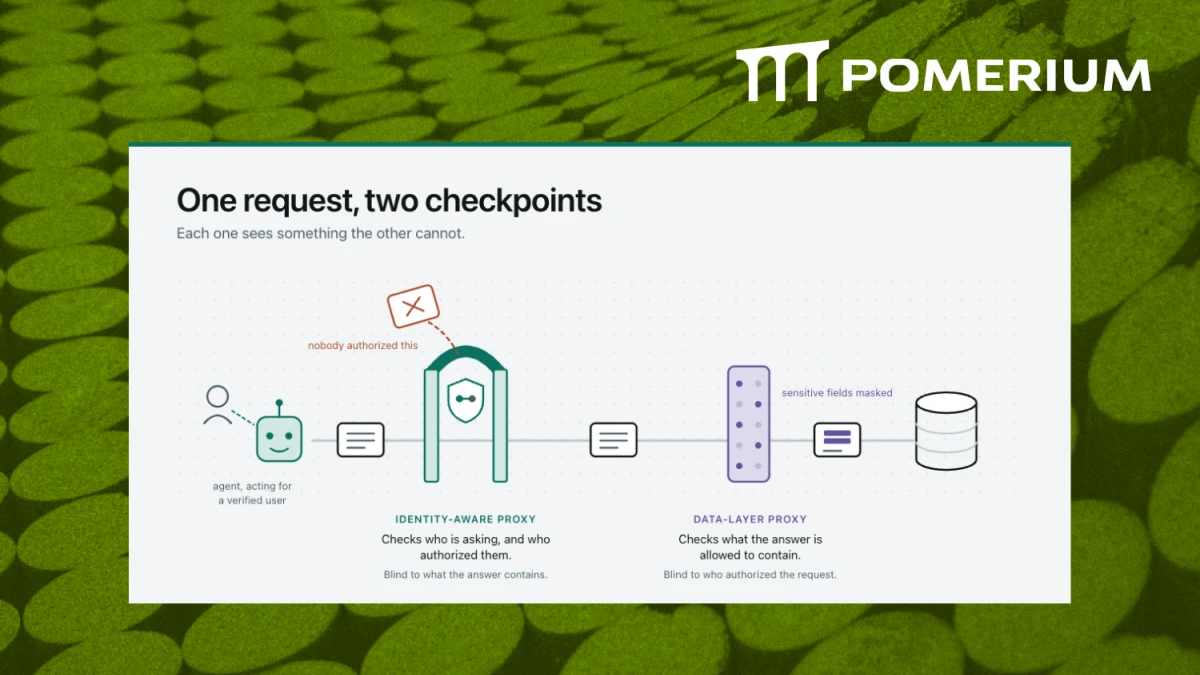
Each time a user or service tries to access a resource, Pomerium checks identity, role, group membership, time of day, and any custom signals you define with your policies.
This ensures that:
The heart of Zero Trust is continuous verification. Without per-request authorization, that promise falls apart:
Pomerium enforces policies at the application layer, in real time, for every request. No traffic rerouting, app rewrites, or third-party data exposure.
Per-request policy isn’t niche. It’s critical across modern infrastructure:
Pomerium is an identity-aware proxy that enforces policies on every request, before requests reach your app or service.
This means:
Every access decision is logged. Every request can be traced.
That’s not just helpful for incident response. It’s essential for proving:
Pomerium’s model helps meet requirements for SOC 2, HIPAA, ISO 27001, and NIST 800-53, without bolt-on tools or separate agents.
Per-request authorization isn’t hard to implement. With Pomerium, it’s built in.
-> Secure your first route with Pomerium
-> Read how companies apply policy in real-time
Access shouldn’t be granted once and forgotten. Give every request the scrutiny it deserves with Pomerium.